
AWS Well-Architected Agent: The Cloud Review Still Needs an Owner
AWS has introduced an AI agent that can inspect a cloud environment, rank architectural problems and supply code or command-line instructions to help fix them. This is useful. It is also the precise moment at which somebody will be tempted to rename a generated recommendations page `the architecture review' and consider Thursday afternoon unexpectedly free.
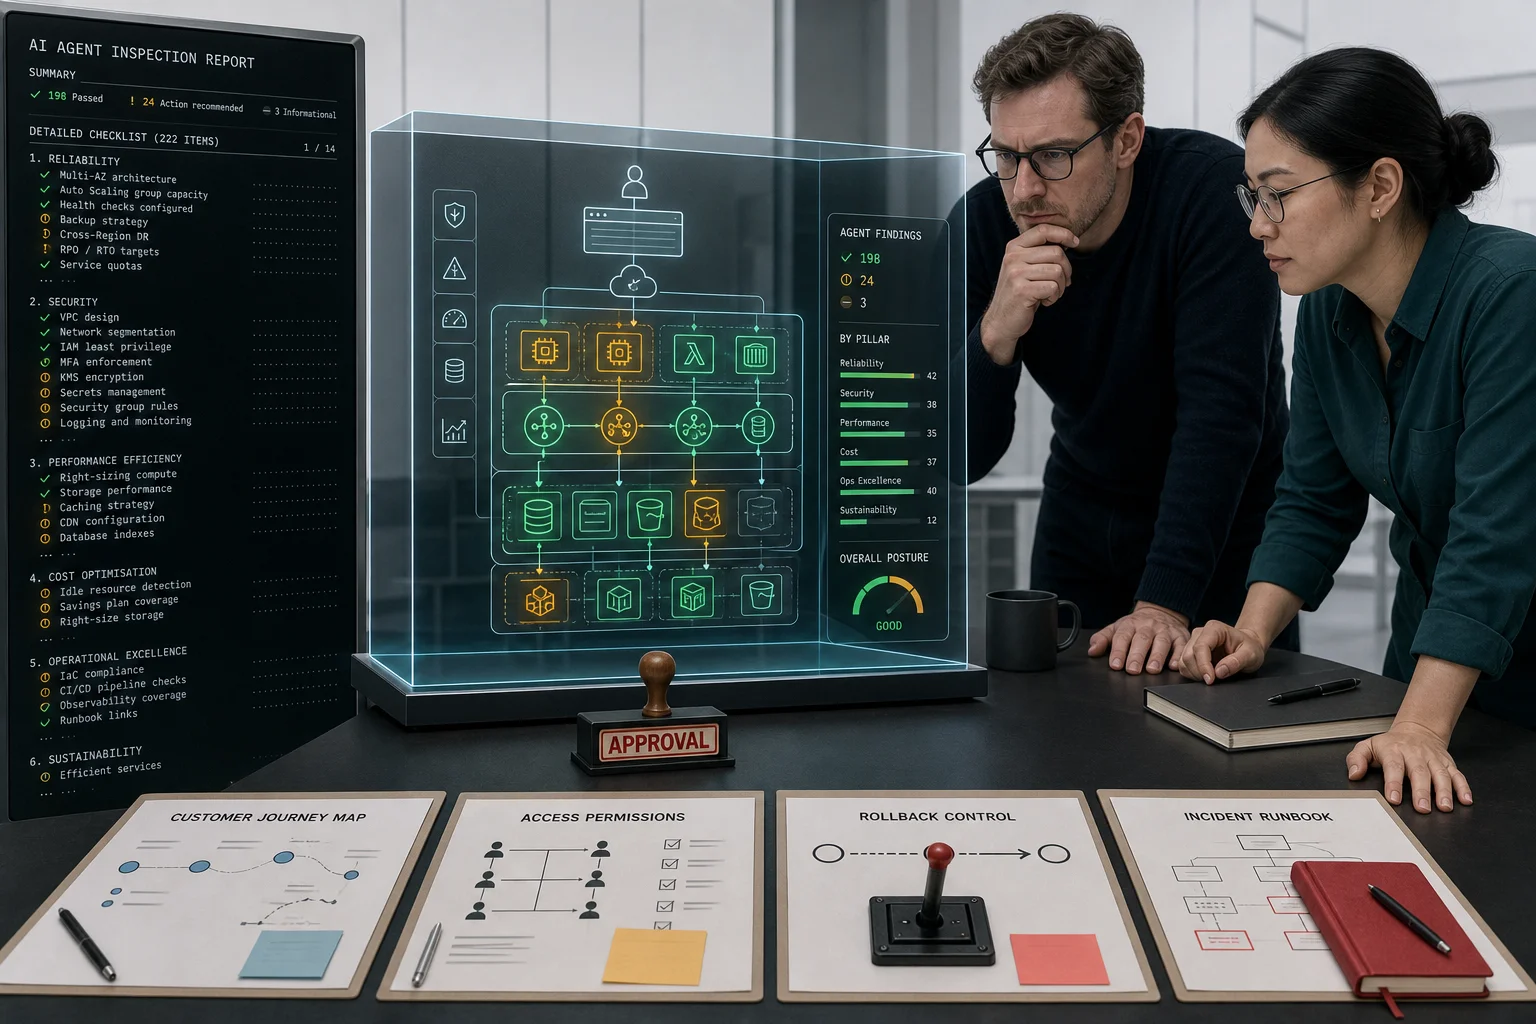
The AWS Well-Architected Agent, announced in public preview on 1 October 2026, analyses resource configurations, utilisation metrics and application topology. AWS says it can assess more than 65 services, relate findings to business goals and suggest changes across cost, security, performance and resilience.
For founders with an AI-built product on AWS, that could turn an intimidating cloud estate into a useful list of work. It does not turn the product into a safe, reliable business by inspection. The agent can tell you a great deal about the machinery. Customers remain stubbornly interested in whether the journey works.
What the AWS Well-Architected Agent actually does
The preview produces recommendations at three levels. It can identify an issue with an individual resource, combine related findings across an application, and propose broader architectural changes. Recommendations may include console instructions, AWS command-line commands or amended Infrastructure as Code, meaning the files used to define and reproduce cloud resources.
Teams can also upload Terraform, AWS CloudFormation or AWS Cloud Development Kit projects for a pre-deployment review. The service then assesses the proposed infrastructure against a selected Well-Architected lens before it reaches production. That is a sensible place to find an expensive design choice: while it is still text in a pull request rather than an invoice with emotional depth.
The agent can prioritise work against declared goals. A team focused on resilience may receive a different order from one trying to reduce cloud spending. AWS also says recommendations expose trade-offs across the relevant pillars, which matters because architecture is rarely a collection of independent green ticks. Extra redundancy can improve availability while increasing cost and operational complexity. Cheaper infrastructure can become impressively expensive during an outage.
Read-only access is a good boundary, not the end of the discussion
AWS's access documentation says the agent uses customer-managed identity and access management roles. For multi-account reviews, an execution role assumes access roles in the target accounts. AWS recommends running the profile from a dedicated account, monitoring activity in CloudTrail and regularly reviewing which accounts remain in scope.
The managed scanning policy uses read-only actions. According to the security documentation, the agent reads telemetry, usage patterns and configuration data but does not read the contents of data stores such as database records or objects in Amazon S3. It cannot create, modify or delete resources through that scanning policy.
Those are worthwhile controls. They also need configuring. A founder should know which accounts, regions and resources the agent can inspect, who may change its profile, and where its findings are retained. `Read-only' means the service should not alter the workload through its discovery permissions. It does not mean the information it can see is commercially unimportant.
AWS states that AI-generated remediation is supplied for review and validation rather than executed automatically. Some remediation based on AWS Trusted Advisor checks can use tested Systems Manager runbooks with the customer's consent. The distinction is crucial: a suggested infrastructure change is not a harmless suggestion once somebody applies it to the live environment.
Why an AWS recommendation is not a production decision
AWS is admirably direct about the boundary. Its launch announcement says generated recommendations may contain errors or incomplete information and that customers must evaluate them in context. The wider AWS Well-Architected Framework describes an architecture review as a constructive conversation, not an audit mechanism.
This is not timid legal decoration. Cloud architecture involves business facts that cannot be inferred reliably from resource settings alone. A recommendation may be technically sound and still be wrong for the product because:
- a database contains regulated or contractually restricted data;
- a proposed change breaks a third-party integration or recovery procedure;
- a lower-cost service cannot meet a customer's response-time requirement;
- the application assumes a particular network path, region or storage behaviour;
- the team cannot operate the more elaborate architecture being proposed.
There are also product risks beyond an infrastructure review. The agent cannot establish from cloud topology alone whether refunds are calculated correctly, whether one customer can see another customer's records, whether the mobile checkout is usable, or whether support knows what to do when an integration fails. Those questions require application testing, access-control review, operational evidence and people who understand the commercial promise.
This is the same distinction explored in Venturist's guide to moving an AI prototype into production. Hosting is part of production readiness. It is not a synonym for it.
How founders should use the AWS Well-Architected Agent
The useful response is neither blind acceptance nor ceremonial suspicion. Treat each recommendation as a well-informed engineering proposal that must earn its way into a release.
- Define the workload and the goal. Record which customer journey the infrastructure supports, its data sensitivity, expected demand, recovery target and cost constraints. An agent prioritising against vague goals will produce precisely prioritised vagueness.
- Keep access deliberately narrow. Use dedicated roles, include only the accounts and resources needed for the review, log activity and remove access that is no longer required.
- Trace each finding to evidence. Confirm the affected resources, the underlying metric or configuration, the expected benefit and the trade-offs. Separate urgent risks from useful housekeeping.
- Review generated code as code. Put amended infrastructure files through version control, peer review and automated checks. Never paste a command into production merely because it arrived wearing an AWS badge.
- Test in a representative environment. Exercise critical journeys, integrations, permissions, performance and failure behaviour. Confirm monitoring and alerts still work after the change.
- Make rollback concrete. Identify the previous configuration, the data consequences of reversing the change, the rollback trigger and the person authorised to act.
- Record the decision. Keep the recommendation, review, test results, approval and release reference together. This creates evidence for support, enterprise customers and technical due diligence.
What launch-ready looks like after the scan
A launch-ready product may still have architectural findings. Real systems involve trade-offs, phased improvements and accepted risks. The important difference is that the team knows what those risks are, why a decision was made, how the product was tested and who owns the next action.
The AWS Well-Architected Agent could make that work faster and more continuous. Weekly recommendations are more useful than a review document that has been gently ageing in a shared drive since the company had three customers. Pre-deployment analysis can also catch cloud mistakes before they become live incidents or recurring costs.
But an automated review remains one input to product readiness. The architecture must be considered alongside the codebase, database rules, customer journeys, integrations, deployment process, monitoring, backups and operational ownership. The cloud can be beautifully arranged while the password reset emails nobody and the payment webhook retries until morale improves.
The Venturist perspective
For founders, the new service is best understood as an unusually capable inspection tool. Use it to surface questions and accelerate remediation. Do not ask it to supply the organisational confidence that only testing, evidence and accountable decisions can provide.
Venturist reviews the whole AI-built product, including its application behaviour, permissions, infrastructure, deployment arrangements and ability to survive ordinary customer use. If the AWS Well-Architected Agent has produced a formidable list of recommendations, or your cloud setup has never received that much attention, show Venturist what you have built. A free introductory product audit can turn the findings into a practical launch plan, with a human owner attached.